You open your site and something’s off. A strange redirect. A red warning screen from Google. A hosting email with the word “suspended” in the subject line.
Website disaster recovery and malware removal can feel like a job for a big IT team. Small business sites get hit every day, because bots scan the web for old plugins and weak passwords and don’t care who owns the site.
The good news: most hacked websites come back. The bad news is that the first few hours matter a lot, and the wrong move can make things worse.
Here’s the plan I’d follow: spot the hack, contain it, clean it, restore the site and close the door behind you. You can handle a lot of it yourself. A few parts you probably shouldn’t.
Work through it in order. If your site is down right now, skip to the first-hour checklist.
Signs your website has been hacked
Some hacks are loud. Others sit quietly for weeks, sending spam or siphoning off your visitors. Check for both.
Visible warning signs
These are the ones you’ll notice first:
- A browser warning such as “Deceptive site ahead” or a “This site may be hacked” label in Google results
- Visitors sent to pharmacy, casino or adult sites you’ve never heard of
- Pages that look defaced, or pop-ups you didn’t add
- A suspension notice or malware email from your host
- Your admin login suddenly refuses your password
Hidden warning signs
These take more digging:
- Admin users you don’t recognize in your dashboard
- A traffic drop with no clear reason, or a spike from countries you don’t serve
- Thousands of new pages in Search Console, often in Japanese or full of product spam
- A slow site and high server load
- Bounced emails you never sent, or customers reporting spam from your domain
- Files with recent modified dates that nobody on your team touched
How to confirm it fast
Start with the Security issues report in Google Search Console. It shows what Google has flagged.
Then run a free external scan such as Sucuri SiteCheck, and look up your domain in Google’s Safe Browsing site status tool.
One more thing. Visit your site while logged out, on your phone’s mobile data, after clicking through from a Google search. Some malware hides from site owners and only attacks everyone else.
What to do in the first hour
Speed matters. Panic costs more. Do these in order.
- Take the site offline or switch on maintenance mode. This stops visitors from catching malware and stops spam pages from getting crawled.
- Back up the infected site. Copy all files and the database, and label the folder “infected.” You’ll want it later to work out how the attacker got in.
- Call your host. Many hosts can scan the account, share server logs and restore a clean snapshot. Ask what they can see.
- Change every password from a clean device. That covers hosting, SFTP, database, CMS admin and the email account tied to your admin login. You’ll change them again after cleanup.
- Screenshot everything. Warnings, odd pages and error messages all help whoever cleans the site, and they help your insurer if you have a cyber policy.
- Pause anything that sends traffic to the site. Ads, email campaigns and social posts only send more people to a broken page.
If you take payments, contact your payment provider too. And if customer data may have been exposed, move to the breach steps in the recovery section below.
Don’t start deleting files yet. Deleting without a plan is how people wipe out the evidence and miss the backdoor.
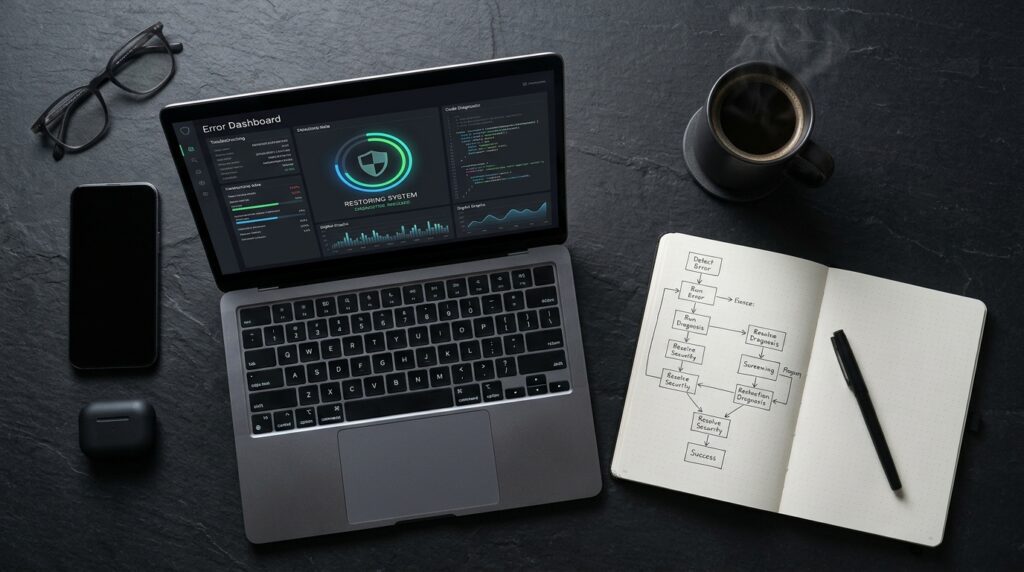
Website disaster recovery and malware removal: the step-by-step process
Disaster recovery means getting a working, safe site back. Malware removal is one piece of it. Here’s the full sequence.
Step 1: Decide whether to restore or clean
You have two routes.
Restore from a clean backup. This is the fastest option if you have a copy from before the infection. The catch is timing. Attackers often sit inside a site for days or weeks, so a backup from last night may already carry the backdoor.
Clean the site in place. This is slower, but you keep recent orders, posts and form entries. You also have to find every infected file.
My rule of thumb: if you can prove a backup predates the first sign of trouble, restore it and patch right away. If you can’t, clean in place or rebuild the core files from fresh copies.
Step 2: Check whether data was exposed
Look for new admin accounts, exported user tables and strange scripts on checkout or login pages. Payment skimmers hide in exactly those spots.
If personal information may have been exposed, you might have legal duties. In Canada, PIPEDA requires organizations to report breaches of security safeguards that pose a real risk of significant harm and to tell the people affected. US states have their own notification laws.
Rules differ by place and by industry, so ask a lawyer or your insurer early.
Step 3: Find how they got in
Cleaning without finding the entry point is like mopping a floor under a leaking pipe. Common causes:
- Outdated plugins, themes or CMS core files
- Weak or reused passwords
- Pirated (“nulled”) themes and plugins that ship with hidden code
- Stolen logins from a staff member’s infected computer
- Other sites on the same shared server, if one of them was compromised
Ask your host for access logs. Look at the timestamp of the earliest modified file and read what happened in the logs just before it.
How to remove malware from your website
Work on the offline site or a staging copy. The examples below use WordPress because it’s the most common platform, but the logic fits any CMS.
Replace core files with fresh ones
Download a clean copy of your CMS from the official source. Replace the core folders and root files, but leave your content folder and config file alone for now.
If you have command line access, WP-CLI can compare your files against the official versions:
wp core verify-checksums
wp plugin verify-checksums –all
Anything that fails the check was changed, and you want to know why.
Reinstall plugins and themes
Delete each plugin and theme, then reinstall from the official source. Remove anything you don’t use. Remove anything pirated too, since those “free premium” downloads are a classic way in.
Hunt for backdoors
A backdoor is a small hidden file or code snippet that lets the attacker walk back in after you clean up. Missing one is the top reason sites get hacked again within days.
Files that don’t belong
Check the uploads folder first. It should hold images and documents, not PHP files. Then look at files with recent modified dates that nobody on your team edited, plus odd filenames that imitate real ones.
Code that looks wrong
Search for functions attackers love, like eval, base64_decode and gzinflate. On a server you can run:
grep -rl “base64_decode” wp-content/
Some legitimate plugins use these functions too, so check every hit before you delete it. Pay special attention to your config file and your .htaccess file. Both are favourite hiding spots.
Clean the database
Back up the database first. Then look for admin users you don’t recognize and delete them.
Search your posts and settings tables for injected <script> and <iframe> tags, plus spam links hidden in old content. Hackers often plant these in the database because file scans skip it.
If you’re on Shopify, Wix or Squarespace
These hosted platforms handle the server side, so attacks usually go after staff accounts and third-party apps. Reset passwords, remove staff accounts you don’t need, review installed apps and look through your theme code for scripts you didn’t add. Then contact platform support.
Restoring your site and getting off blocklists
The site looks clean. Don’t flip the switch yet.
Lock the doors before going live
Change every password again, now that the backdoors are gone. That includes hosting, SFTP, the database and every admin account. Update the database password in your config file after you change it.
Generate new security keys and salts if you run WordPress. This logs out every active session, including any the attacker still holds.
Update the CMS, plugins and themes to their latest versions. Then run another scan and check your logs for a day before you trust the result.
Clear the warnings
If Google flagged your site, open the Security issues report in Search Console. Fix what it lists, then request a review. Reviews usually take a few days, so a lingering warning doesn’t mean you failed.
If spam pages got indexed, make sure they return a 404 or 410 error. Use the Removals tool in Search Console to hide them from results faster, and submit a fresh sitemap.
Check your robots.txt file and your sitemap too. Attackers sometimes edit them.
Check the other blocklists
Google isn’t the only one. Look up your domain on the Safe Browsing site status page and in your email provider’s reputation tools. If your host suspended the account, send them the cleanup details and ask for reinstatement.
If your emails land in spam since the attack, give it a week or two and test again.
DIY cleanup or a malware removal service?
There’s no shame in calling for help. Plenty of owners should.
Approach | Pros | Cons | Best for |
Do it yourself | Lowest cost and full control | Easy to miss a backdoor. Takes time | Small brochure sites with no customer data and a clean backup |
Your hosting provider | Often free or cheap, and they know the server | Some only restore a backup and skip root cause | First call for every hack |
A malware removal service | Experienced eyes, written report and faster turnaround | Costs money. You’ll share access to your site | Ecommerce stores, reinfections and sites with customer data |
When I’d hire someone
Call a pro if any of these apply:
- You take payments or store customer details (see our guide to website maintenance for ecommerce stores)
- The site got hacked again after a cleanup
- Google or your host has blocklisted you
- Every hour offline costs you more than the service fee
- You can’t find how the attacker got in
What to ask before you hire
A good malware removal service should answer these without dodging:
- Do you find the root cause, or only delete bad files?
- Will I get a written report of what was found and fixed?
- Is there a reinfection guarantee, and how long does it last?
- Do you handle the Google review request?
- What access do you need, and can I give you a temporary account?
Be wary of anyone promising a full cleanup in minutes without scanning anything. Be wary too of anyone who wants your main hosting password when a limited account would do.
Build a website backup and restore plan
A backup you’ve never restored is a hope, not a plan. Here’s how to build one that works on a bad day.
Follow the 3-2-1 rule
Keep 3 copies of your site, on 2 different types of storage, with 1 copy off the server. If your only backups live on the same hosting account as the site, an attacker who gets in can wipe both.
Decide what to back up and how often
Back up the files, the database and your config. Also write down your DNS records and email settings somewhere safe, because they’re painful to rebuild from memory.
Frequency depends on how often your site changes:
- Online store or busy blog: daily, or even more often for orders
- Brochure site: weekly, plus before every update
Keep at least 30 days of history. Slow infections need you to reach back past the first sign of trouble.
Test your restores
Once a quarter, restore a backup to a staging site and click around. Check that images load, forms send and checkout works. You’ll find problems now instead of at 2 a.m. during an attack.
Write the plan down
Two questions shape everything: how long can the site stay down, and how much recent data can you afford to lose? Your answers set your backup schedule.
Then put a one-page plan in a shared folder. List who calls the host, where the logins live, who can approve spending and who tells customers. Add your host’s emergency contact and your domain registrar’s login.
This is the heart of any website backup and restore plan. Our website backup and disaster recovery guide goes deeper on the technical side. When the site goes down, nobody wants to hunt for a phone number.
How long hacked website recovery takes
It depends on the size of the site and how deep the infection runs. Here are typical ranges for a small business site.
Stage | Typical time | What happens |
Containment | First hour | Site offline, backup taken, host contacted, passwords changed |
Diagnosis | A few hours | Scans, log review and a decision to restore or clean |
Cleanup | Several hours to 2 days | Core files replaced, backdoors removed, database checked |
Hardening and relaunch | Half a day to 1 day | New passwords, updates and a final scan |
Google and blocklist review | A few days | Review request submitted and warnings cleared |
Search traffic recovery | Weeks, sometimes longer | Rankings return as Google recrawls clean pages |
Large stores and sites with years of spam pages take longer. A clean backup and a written plan can cut the first three stages dramatically.
Traffic is the slow part. Even after the warnings disappear, rankings need time to return, so keep publishing and keep your site fast while you wait. If rankings stay flat for weeks, our SEO services can help, and our guide on why your website isn’t ranking covers the first fixes.
How to stop your site getting hacked again
OWASP’s Top 10 list of web risks includes vulnerable and outdated components, and that matches what shows up in real cleanups. NIST’s Cybersecurity Framework also treats recovery as a core function next to protecting and detecting. You need all of them.
Here’s what I’d put in place first (our website security guide goes deeper):
- Update on a schedule. Check plugins, themes and core files weekly. Turn on automatic updates for security releases. Our WordPress website maintenance guide shows how.
- Delete what you don’t use. Every inactive plugin is still code an attacker can target.
- Use a password manager. Every account gets a long, unique password.
- Switch on two-factor authentication. Do it for your CMS, hosting, domain registrar and email.
- Give people the least access they need. A blog writer doesn’t need admin rights.
- Add a web application firewall. It blocks known attack patterns before they reach your site.
- Turn on file change alerts. You want an email the moment a core file changes.
- Switch off the file editor in your dashboard. In WordPress that’s one line in your config file.
- Pick decent hosting. Cheap shared servers with no isolation between accounts are a recurring problem.
Staff matter too. Many hacks start with a phishing email, so teach your team to check the sender before they click anything. And if constant patching wears you out, an older site may cost less to rebuild than to keep fixing. Our website design and development team builds on current platforms.
Put a monthly 30-minute reminder in your calendar and run through the list. It’s boring. It works. If you’d rather hand the list off, our website maintenance and security plans cover updates, backups and monitoring.
Common mistakes that cause a second hack
These show up again and again.
- Fixing the symptom. Removing the spam redirect while leaving the backdoor that created it. The redirect is back by Friday.
- Restoring a backup without patching. The same weak plugin lets the attacker straight back in.
- Trusting one scanner. A single plugin scan misses things. Combine a server-side scan, a file comparison and a manual look at the usual hiding spots.
- Skipping the password reset. If the attacker has your logins, they don’t need malware at all.
- Ignoring the Google warning. Leaving a flagged site alone costs you traffic every day.
- Staying quiet. If customer data was exposed, silence makes things worse. Tell the people affected, and take legal advice on what the law requires.
One more: installing a pirated plugin to “fix” the problem. Pirated code often carries its own hidden backdoor, so that move can turn a small hack into a long one.
Conclusion: get ready before the next attack
Website disaster recovery and malware removal come down to order and speed. Contain the site, find the way in, clean everything and lock the doors behind you.
If you’re in the middle of an attack right now, start with the first-hour checklist and call your host. If your site is fine today, set up an offsite backup and test one restore this week.
Want an expert to handle it? Contact our team for a malware scan and a written quote. We’ll tell you what we find and what the fix involves.